
AgentOps
Identity for AI agents: who they are and what they access
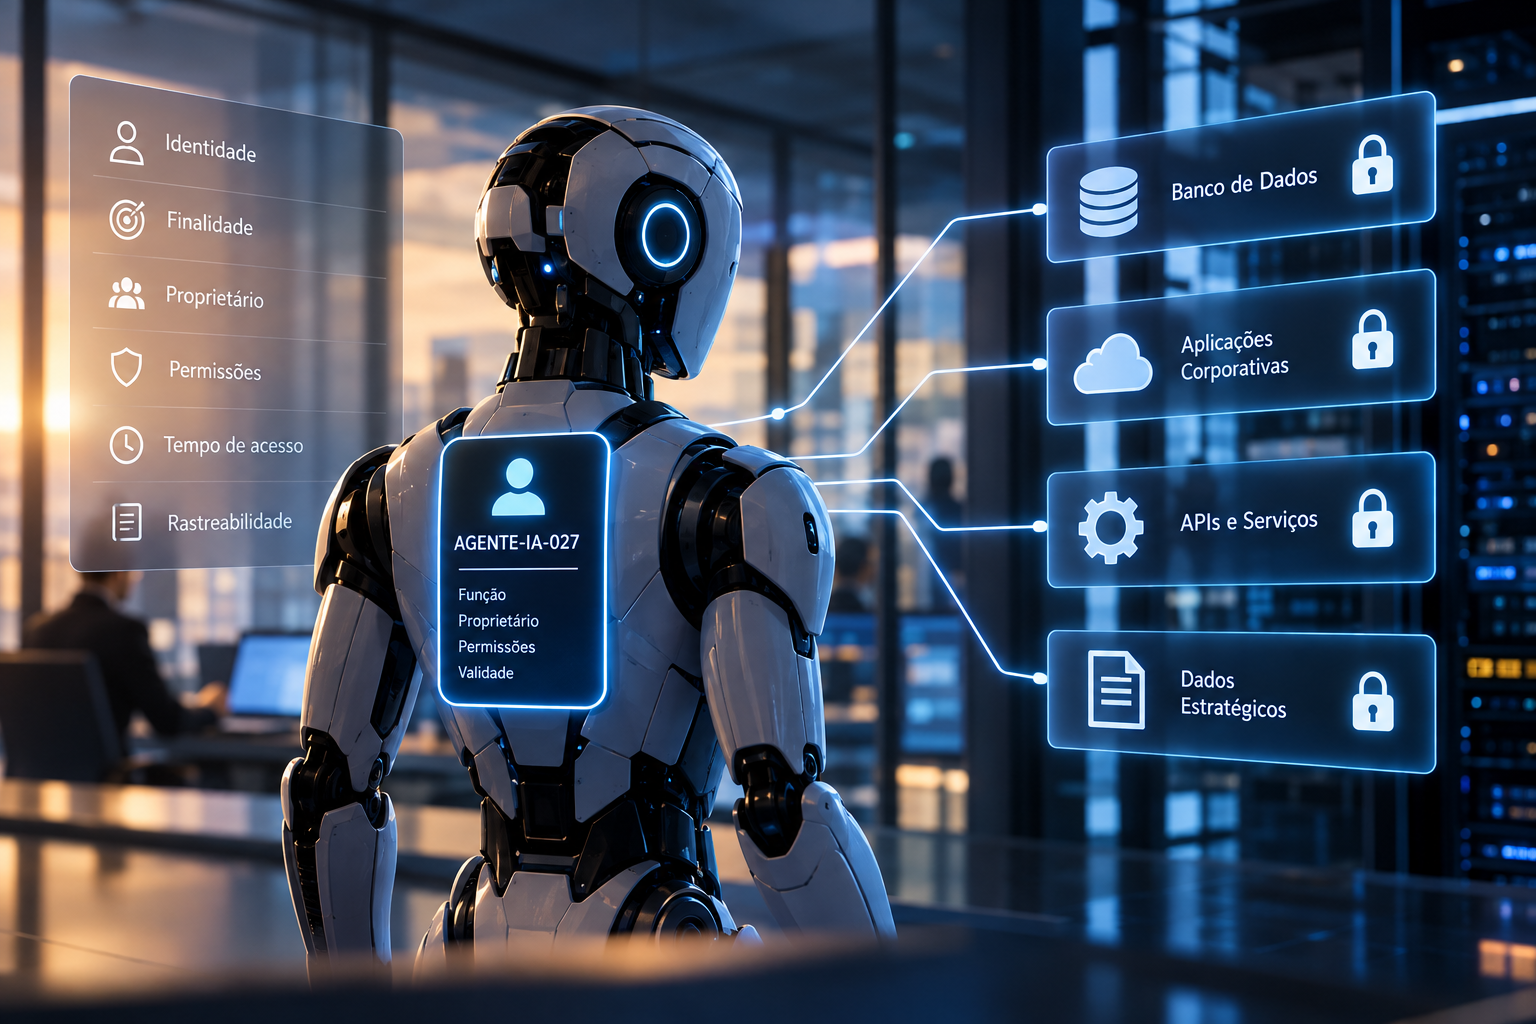
When a person logs in to a corporate system, there is normally an identity tied to that access. The company knows, or should know, who the user is, which resources they can use, which permissions they hold, and, when necessary, it can revoke their access.
With artificial intelligence agents, that relationship becomes more complex. They can access applications, query data, use tools, call application programming interfaces, interact with other agents, and execute actions across different systems. All of this can happen on behalf of a person, a department, or the organization itself, often without an individual, clearly governed identity for each agent.
The problem tends to grow quickly with scale. Gartner estimates that the average global Fortune 500 company could go from fewer than 15 agents in use in 2025 to more than 150,000 in 2028 [1].
In just three years, a large company could go from fewer than 15 to more than 150,000 agents in operation. In the same study, only 13% of organizations say they have adequate governance for AI agents [1].
Managing a population of that size will require more than knowing that a given agent exists. It will be necessary to identify who it is, what its purpose is, who is accountable for it, on whose behalf it is acting, and which resources it can access.
Agents need to stop being invisible identities
For a long time, non-human identities have been part of technology environments. Service accounts, Application Programming Interface (API) keys, certificates, applications, and automated processes need some form of authentication to access corporate resources.
Agents add an important difficulty to this scenario because they are not necessarily limited to running a previously defined sequence. Depending on their autonomy, they can interpret a goal, choose tools, combine information, and decide which steps to take to reach a given result.
That makes it insufficient to treat the agent as just another technical credential.
Okta’s Businesses at Work 2026 research shows the size of this gap. Although 91% of the organizations surveyed already use AI agents, only 10% say they have a well-developed strategy for managing non-human identities [2]. The same research indicates that 78% consider access and permission control for these identities a relevant concern [2].
The issue becomes even more sensitive when different agents use shared accounts, generic credentials, or access originally granted to a person. In those cases, the system may record that a given credential performed an action without necessarily making it possible to identify which agent was behind it, why it received that authorization, or on whose behalf it was operating.
That difference has practical consequences. If several agents use the same technical identity, revoking the access of just one of them can be difficult. It also becomes harder to investigate a specific action or to determine whether a given access is still needed after the agent’s original purpose no longer exists.
PwC recommends treating agents as governed members of the digital workforce, with verifiable identity, a defined role, permissions specific to the task, and auditable records [3]. This makes it possible to tie access not only to a credential, but to a purpose and to a responsible party.
An agent that can act on a company’s systems needs to be identifiable as an agent, have a known purpose, and have someone clearly responsible for its existence and actions.
This principle also creates a direct bridge to accountability. In the article Accountability in Agentic AI: who answers when an agent makes a wrong decision?, we discussed that delegating an action does not eliminate responsibility for the consequences. For that chain to be reconstructed, the first step is being able to correctly identify who carried out each action.
Knowing who the agent is does not mean letting it access everything
Identity and authorization are deeply related, but they are not the same thing. Knowing exactly which agent is trying to access a given resource does not mean it should be allowed to do so.
An agent created to query customer data may need to access certain information during a task and have no reason to change that data. Another may receive temporary authorization to execute a specific action and lose that access as soon as the work ends. In both cases, the identity stays the same, while permissions vary according to purpose, context, and risk.
This is precisely where traditional models begin to be pressured. People normally hold relatively stable roles within the organization, while conventional applications tend to run previously programmed behaviors. Agents can combine traits from both worlds: they are given authority to act, but have the flexibility to choose how to carry out a task.
Boston Consulting Group (BCG) calls this difficulty the authorization gap. According to the consultancy, 35% of the organizations surveyed already have Agentic AI in production, 44% plan new deployments, and more than a third expect to grant agents independent decision rights within three years [4]. (BCG Global)
The central point of BCG’s analysis is that controlling only the resource accessed may not be enough. Authorization also needs to consider the purpose for which the agent received authority and the limits on how it may pursue that goal [4].
Identifying the agent answers the question “who is trying to act?”. Governing its access also requires answering “on whose behalf, for what purpose, with which permission, and for how long?”.
This shift favors a more dynamic approach. Instead of granting broad, permanent access just because a given agent might need it at some point, the organization can bring authorization closer to the task actually being performed, reducing unnecessary privileges and revoking permissions when they no longer make sense.
Scale makes this discussion even more relevant. If tens or hundreds of thousands of agents begin to operate inside a large organization, authorization processes based exclusively on manual reviews will struggle to keep up with the speed of change.
Okta found that access requests per company grew more than twelvefold in two years, while access certifications increased more than ninefold [2]. For the company, the expansion of agents intensifies the need for governance models capable of operating at a speed compatible with automated systems.
When access requests grow more than 12 times in two years, managing identities and permissions with manual processes alone stops being only an efficiency problem and becomes a scale problem [2].
Identity is a foundation for governance, traceability, and trust
As agents begin to take part in corporate processes, their identity starts to serve a function that goes beyond access security. It becomes one of the references needed to reconstruct what happened during an execution.
When an incident occurs, knowing that an application was accessed is not enough. The organization may need to determine which agent performed the action, which task it was executing, who had delegated that authority, which permissions were valid at that moment, and which other agents or tools took part in the process.
BCG argues that, when an agent acts, the environment should be able to identify the agent itself, the person or business function on whose behalf it operates, and the purpose for which that authority was delegated [4]. This connects identity directly to the chain of responsibility.
It also means the agent’s lifecycle needs to be governed. Agents may be created for temporary projects, have their purpose changed, receive new tools, or stop being needed. If their identity and permissions remain active after that, the organization accumulates access with no current operational justification.
The problem becomes even more relevant in multi-agent environments. One agent may delegate part of a task to another, which in turn uses a tool or accesses a service. Preserving identity and authority along that chain makes it possible to distinguish who started the task, who received it, and which limits should remain valid during the delegation.
Without its own traceable identity for each agent, the company may be able to record that an action happened, but will have more difficulty explaining who actually executed it, under which authority, and for what purpose.
This does not simply mean replicating for agents all the mechanisms built for employees. Agents operate at a different speed, can be created in large numbers, work continuously, and interact with one another. Identity governance needs to recognize these differences without giving up principles that remain essential: identification, ownership, least privilege, traceability, and revocation.
Identity thus works as a kind of connection point between security, governance, and accountability. The more autonomy is granted to agents, the more important it will be to tie each action to a known identity and to the authority that allowed it to be executed.
From vision to practice: ARGUS
This need to relate identity, authority, access, and behavior is directly connected to the proposal of ARGUS as a platform for Operational and Agentic Intelligence.
With AgentOps (Agent Operations) and AI Gateway capabilities, ARGUS seeks to help the actions of agents be governed and observed within a common operational layer. Identities, policies, permissions, tool calls, decisions, and results become part of the context needed to understand how each agent is acting.
ARGUS does not replace the specialized corporate platforms for Identity and Access Management (IAM). The proposal is to use and relate that information to the execution of agents, to the applicable policies, and to the operational context in which their actions take place.
This distinction is important. Knowing that a given agent has an identity and a permission is one part of the problem. When it actually uses that authorization, we also need to understand what was happening in the operation, which task was being executed, which tools were called, and what consequences that action produced.
By correlating information from multiple sources, ARGUS seeks to build this shared operational context, connecting people, agents, automations, applications, infrastructure, and services within a systemic view.
As the agent population grows, this capability can help organizations prevent each agent from becoming yet another silo of intelligence and control. Identity stops being only the credential used to log in to a system and becomes part of understanding who is acting, under which authority, and within which context.
Learn about ARGUS and see how it works in practice.
About the author
Paulo Florêncio de Menezes is an entrepreneur, partner, and co-founder of companies such as Target Solutions, BiPTT, and ARGUS.
He holds a degree in Data Processing from the Federal University of Amazonas (UFAM), an MBA in Business Management from Fundação Dom Cabral (FDC), and a Professional Master’s in Economics from Fundação Getulio Vargas (FGV).
In his Master’s research, he developed the IBEOP-IA (Brazilian Index of Potential Occupational Exposure to Artificial Intelligence), investigating the potential exposure of Brazilian occupations to AI capabilities by combining occupational data, artificial intelligence patents, and natural language processing techniques.
References
[1] Gartner. Gartner Identifies Six Steps to Manage AI Agent Sprawl. Apr. 28, 2026.
[2] Okta. Businesses at Work 2026: Closing the identity gap in the age of AI. Apr. 30, 2026.
[3] PwC. AI agents as workforce counterparts---what governance should look like. Jul. 17, 2026.
[4] Boston Consulting Group. The Authorization Gap: Why Yesterday’s Controls Won’t Work with Today’s Agents. Sep. 22, 2026.